Raam Dev

Hello, future.

Fixing Boot-Time Dialog Display Issues

Dialog is a really useful utility for creating professional looking dialog boxes and menus within a shell script. I'm working on a boot-time script that allows the user to make system-level changes before the system has fully booted.

When testing my script from the command line, the dialog menu looked fine. However, whenever I set the script to start during boot (update-rc.d myscript.sh defaults, on Debian-based systems) here is what the menu looked like:
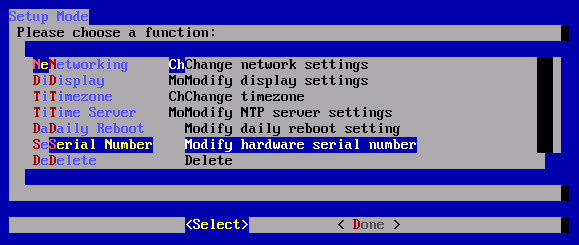
dialog display issues

UGH! It was barely usable. At first, I thought this would be an endlessly difficult problem to solve given my limited in-depth knowledge of Linux (I'm getting there!), but then I realized the main difference between the script running during boot and the script running after I had logged in was that my environment variables had not been loaded.

From the command line, I ran the env command to display all my current environment variables:

debian_vm:~# env
TERM=xterm-color
SHELL=/bin/bash
SSH_CLIENT=172.16.168.1 61315 22
SSH_TTY=/dev/pts/0
USER=root
MAIL=/var/mail/root
PATH=/usr/local/sbin:/usr/local/bin:/usr/sbin:/usr/bin:/sbin:/bin:/usr/bin/X11
PWD=/root
LANG=en_US.UTF-8
PS1=h:w$
SHLVL=1
HOME=/root
LANGUAGE=en_US:en_GB:en
LOGNAME=root
SSH_CONNECTION=172.16.168.1 61315 172.16.168.132 22
_=/usr/bin/env

The three variables that caught my eye were TERM, SHELL, and LANG. After a little trial and error, I discovered setting the LANG variable fixed the display issues with dialog! I added the following near the top of my script:

export LANG=en_US.UTF-8

Now when my script loads during boot, everything looks correct:
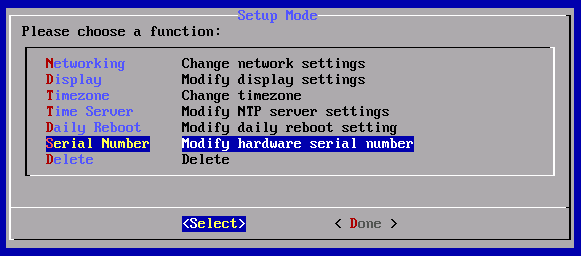
dialog display issues fixed

I Killed a Bird Yesterday

I killed a bird yesterday. He was dancing around on the road in front of me, trying to catch a bug in mid-air. He was so preoccupied by the bug he didn't see my big Chevy heading straight for him at 40 MPH. BAM! I glanced in my rearview mirror to see him laying motionless on the ground. I thought about his last few seconds; he was probably hungry.

Using CURL to Upload Files via POST to Amazon S3

A few months ago I wrote a post about creating Amazon S3 HMAC Signatures without PEAR or PHP5. One of the things I was using that PHP script for was to feed the necessary information to a bash script hosted on a remote machine. The bash script was to upload a file via POST to Amazon S3 using the information provided.

Since CURL was already installed on the remote machine, I wanted to use that to do the actual uploading. I found very little help on the net regarding how to do this with CURL so here you go:

eris:~ raam$ curl
-F "key=screenshots/current_screenshot.jpg"
-F "acl=public-read"
-F "AWSAccessKeyId=2EO6H8MX1X8YWEA0V432"
-F "Policy=eyAiZXhwaXshdGlvbpI6ICIyMDA4LTErLTAxVDtyOjAwOjAwLjAsMFoiLAogICJjb25kaXRpb25zPjogWwoJeyJidWNrZXQiOiAiczNwaG90b3MubW9hcHAubmV0IiB9LAogICAgWyJzdGFydHMtd2l0aCIsICIka2V5IiwgIkxpdmVTaG90cy8iXSwKICAgIHsiYWNsIjogInB1YmxpYy1yZWFkIiB9LAoJWyJlcSIsICIkQ29udGVudC1UeXBlIiwgImltYWdlL2pwZWciXSwKICBdCn0K"
-F "Signature=20uh08kU75ADHL49NyhYRgZW8BY="
-F "Content-Type=image/jpeg"
-F "file=@current_screenshot.jpg"
http://screenshots.ekarma.net

Keep in mind this assumes the current_screenshot.jpg file is in your current directory.

Leaving Send2Fax and Switching to FaxPipe

I canceled my Send2Fax account after a visitor to this blog recommended I take a look at FaxPipe and I realized I could be saving some money. When I started using Send2Fax back in 2006 I believe I was paying around $3 a month. Since I signed up, they have increased the price to $12 a month.

I don't send or receive faxes very often (maybe once or twice a month) but it's nice to have such a service. At the same time, it's not something I depend on so if I can save money by switching then I should.

After signing up for FaxPipe I sent in a request to cancel my Send2Fax account. Within 48 hours, I got a response that included this:

Did you know that you can keep your Send2Fax number for just $2.95 per month? This is a great way for you to keep your fax number and it costs less than a cup of coffee! For just $2.95 per month you get to keep your assigned fax number AND get 20 FREE pages each month, while overage pages are just $0.25 per page*.

That's $1.00 a month less than FaxPipe and about the same amount it was costing me when I signed up 2 years ago. This pissed me off because it seemed like they intentionally increased the price over time hoping I wouldn't notice and then offered to lower price again when I was ready to cancel. I sent them a reply saying I still want to cancel and then along with the confirmation I received this:

Before you go, though, we wanted to let you know about an easy way to get an unlimited FREE online fax service through one of our partners, eFax. You can sign up for an eFax Free account and pay nothing at all to receive up to 20 fax pages a month with your own personal eFax fax number.

I looked into this "free" service and not only is it meant to be used as a trial, but the fax number they give you will be outside your local calling area.

If Send2Fax had left the monthly price low in the first place, I would have stayed with them.

My Notes from The Last HOPE

Here are my notes from The Last HOPE. I started taking notes late, so unfortunately I don't have notes from all the talks I attended.

Ghetto IDS and Honeypots
* An Evening with Berferd
* Low interaction honeypots: Nepenthes, honeyd, Honeytrap
* Monitor both Honeyd and Nepenthes with Prelude IDS

Monitoring Snort
* SGUIL
* BASE
* SnortSnarf

Remember, tcpdump (a common packet sniffer) writes data in pcap format which ngrep, WireShark, or Snort can process.

Kevin Mitnick - Featured Speaker
* Flowroute + Asterisks can be used to unmask Caller ID (I tested Mitnick's setup by calling his phone... my blocked number showed up!)

PenTest Labs Using LiveCDs by Thomas Wilhelm
* de-ice.net
* BackTrack, Slax

PenTesting from Firefox URLs:
* isecom.org/osstmm/
* owasp.org/index.php/Main_Page/
* csrc.nist.gov/publications/PubsSPs.html
* vulnerabilityassessment.co.uk/Penetration Test.html
* centralops.net
* nmap-online.com
* hackerwhacker.com (similar to GRC)

Remember, use TOR when doing active tests!

More useful URLs:
* gdataonline.com/seekhash.php
* passcracking.com
* hash.insidepro.com
* md5this.com
* gdataonline.com
* us.md5.crysm.net
* md5.rednoize.com
* milw0rm.com
* freerainbowtables.com
* netcraft.com

Pen Testing the Web with Firefox

Firefox Extensions:
* FireCat
* ExploitMe (XSS-Me, SQL Inject-Me, Access-Me)
* Tamper Data
* Passive Recon
* Add N Edit Cookies
* Firebug
* HackBar
* Web Developer
* xssed.com

Using Firefox as a Front-End: Proxies
* Tor Button
* Paros Proxy
* SPIKE Proxy
* Burp Proxy

Web Frontends
* Metasploit
* FastTrack
* Inprotect (web interface for Nessus and Nmap)
* BASE (web front-end for Snort)

Use Firefox profile manager to install different selections of extensions to help with memory concerns.

FEBE (Firefox Environment Backup Extension)
CLEO (Compact Library Extension Organizer)
OPIE (Import/Export extension preferences)

Places/Things to hack "safely"
* OWASP WebGoat Project
* PwnOS (VMWare image, requires forum login)
* Your own VMWare lab

Identification Card Security: Past, Present, Future

The Complete Amature - ID Making Operating Guide by Doug Farre

* Epson Stylus R800 photo printer
* Laminator
* Dye cutter
* Magnetic stripe encoder
* Custom rubber stamp (simonstamp.com)
* Black light
* Scanner
* Signature pad
* Photoshop
* Brainstorm ID Supply

Minimal needed materials:
* Teslin Paper
* Pearl-Ex pigment powders
* Ultraviolet pigment powder
* Transparent base

(Get these from practicingperfection.7p.com. That site is down as of right now, so you need the guy's email address to contact him.)

Documentation on ID security can be found at idsysgroup.com.

Books to Read
* 1491: New Revelations of the Americas Before Columbus
* Hackers: Heroes of the Computer Revolution
* The Art of Intrusion: The Real Stories Behind the Exploits of Hackers, Intruders & Deceivers

Random URLs:
* foodhacking.com
* hackerspaces.org
* telephreak.org

Girl behind me

The girl behind me on the bus was telling her friend a story; suddenly I was visualizing her words & dreaming while partially still conscious; my brain was being fed dream food!

Calling Kevin Mitnick

During Kevin Mitnick's talk, he demonstrated how to unblock CallerID. He announced his phone number, put his iPhone on the big screen, and asked the audience to call him with a blocked number. Being a hacker conference, not many were willing to risk disclosing their number on the big screen to the 800+ people watching. After a long 20 seconds one guy called and sure enough his number showed up.

After some really quick mental risk assessment, I decided to call too, since my number is also blocked and I was curious. Sure enough, my number also showed up on the big screen. (I quickly hung up hoping to prevent anyone from writing it down. No prank calls yet, *knock on wood*.) I added Kevin Mitnick to my phone's contacts list and it's really weird seeing his name in my call history.

Heading to NYC for the Weekend to Attend HOPE

I'm on my way to HOPE (Hackers On Planet Earth) in New York City, a three day event full of geeky tech stuff (and unfortunately it's the last one they're holding in NYC). Figuring out which of the one hundred or so talks to attend was difficult; most of them are happening three at a time (in different rooms) and with so many great topics it was difficult to choose one from the other. But now I have my weekend planned out and it should be fun.

Since my decision to go was made last minute, I was unable to find a hotel cheap enough for my wallet and, as it stands right now, I won't be sleeping for the entire weekend (the reality of that is still sinking in). The entire trip should be pretty cheap, at least compared to the last time I went to HOPE (in 2004). I believe the last time I went it cost me around $600 (bus + hotel + HOPE ticket + food). This time I intend to keep that number under $200.

While I'm in NYC, I might pick up an iPhone at the Fifth Avenue Apple store. While all the other stores around Boston have been out of stock since Sunday, the NYC stores have remained fully stocked.

Stand by for updates from HOPE.